Join our newsletter

New articles on Keycloak, authorization and running IAM in production.

  • ISO 27001

What is Keymate? Keymate is the authorization-first IAM platform. It is complete, self-hosted and built on hardened Keycloak, the CNCF open-source IAM project. Identity Governance and Authorization Governance are modules on top. Policies decide what each request may do. Keymate enforces that decision on every request. The record of each decision is what you show your auditor. It runs entirely on your infrastructure, air-gapped if you need it (Enterprise), and the product reports nothing back to us.

Product

  • Identity
  • Authentication
  • Authorization
  • Identity Governance
  • Authorization Governance
  • Parallel Run
  • Architecture
  • Roadmap
  • Pricing

Compare

  • IAM platform comparison
  • Keymate vs Okta
  • Keymate vs Microsoft Entra ID
  • Keymate vs Ping Identity
  • Keymate vs Keycloak

Why Keymate

  • Why Keymate
  • Access evidence for audits

Company

  • Company
  • Docs
  • Blog
  • Contributions
  • Careers
  • Support
  • Contact

© 2026 Keymate Inc. · the authorization-first IAM platform

  • Terms of Use
  • Privacy Policy
  • Cookie Policy
  • Information Security Policy
Keymate
  • Pricing
  • Blog
Book a demo

Devops - Keymate Blog

Categories

Best PracticesDevOpsEngineeringGetting StartedIdentity & SecurityKeymatePerformanceSecurity
← Back to All Posts

Category: Devops

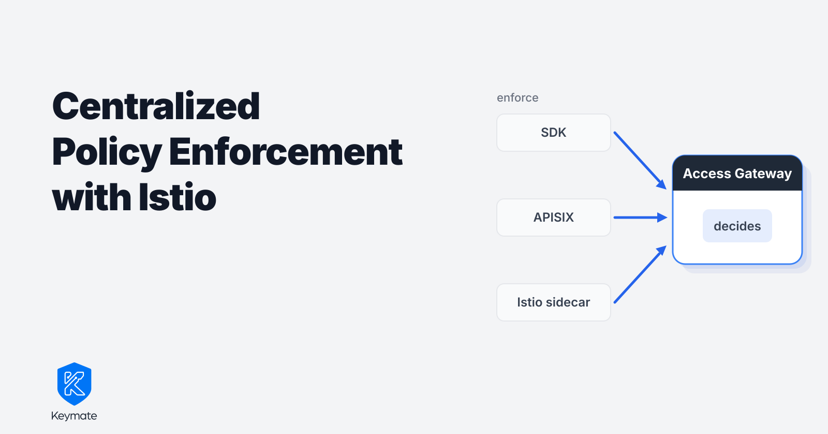
Centralized Policy Enforcement with Istio

Centralized Policy Enforcement with Istio

Istio can enforce an authorization decision at the sidecar. It should not be the place where that decision is made. Here is how a mesh enforcement point hands the decision to one central service, and what fails when the two stop agreeing.
Buket Çoban

October 2026

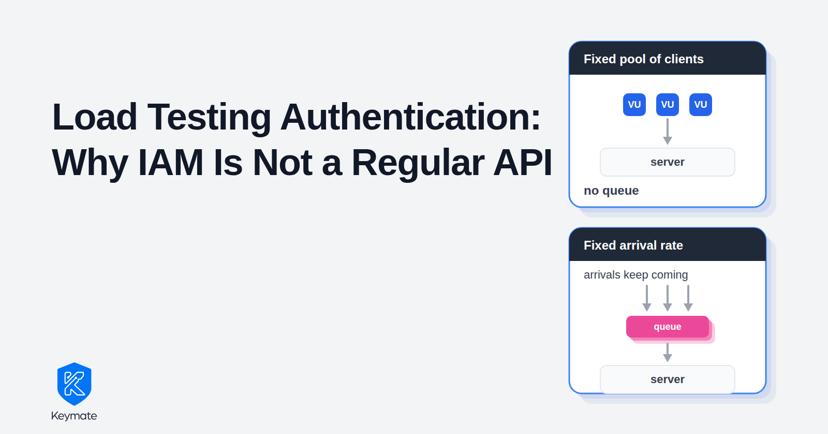
Load Testing Authentication: Why IAM Is Not a Regular API

Load Testing Authentication: Why IAM Is Not a Regular API

A load test can report a healthy system and tell you nothing. Two settings inside the test decide the result before the server does, and the useful output is not a number but a number plus the conditions that produced it.
Buket Çoban

September 2026

Runtime Protobuf Schemas in Keycloak's Embedded Infinispan

Runtime Protobuf Schemas in Keycloak's Embedded Infinispan

Keycloak offers no supported, configuration-only way to load runtime-mounted Protobuf schemas into its embedded Infinispan. This post walks through the extension pattern that bridges that gap through ProtoStream's documented initializer lifecycle, reviewed through a security and platform-engineering lens, with a runnable public demo.
Ali Tuğrul Pınar

July 2026

Beyond the Default Image: Hardening Keycloak for Enterprise Production

Beyond the Default Image: Hardening Keycloak for Enterprise Production

The default Keycloak image is a strong baseline, not a hardened production runtime. Here is how we rebuilt it on Wolfi OS, with three-tier CVE management, non-root execution, and a Quarkus-optimized runtime.
Ali Tuğrul Pınar

April 2026