Keymate Blog | Articles and Resources
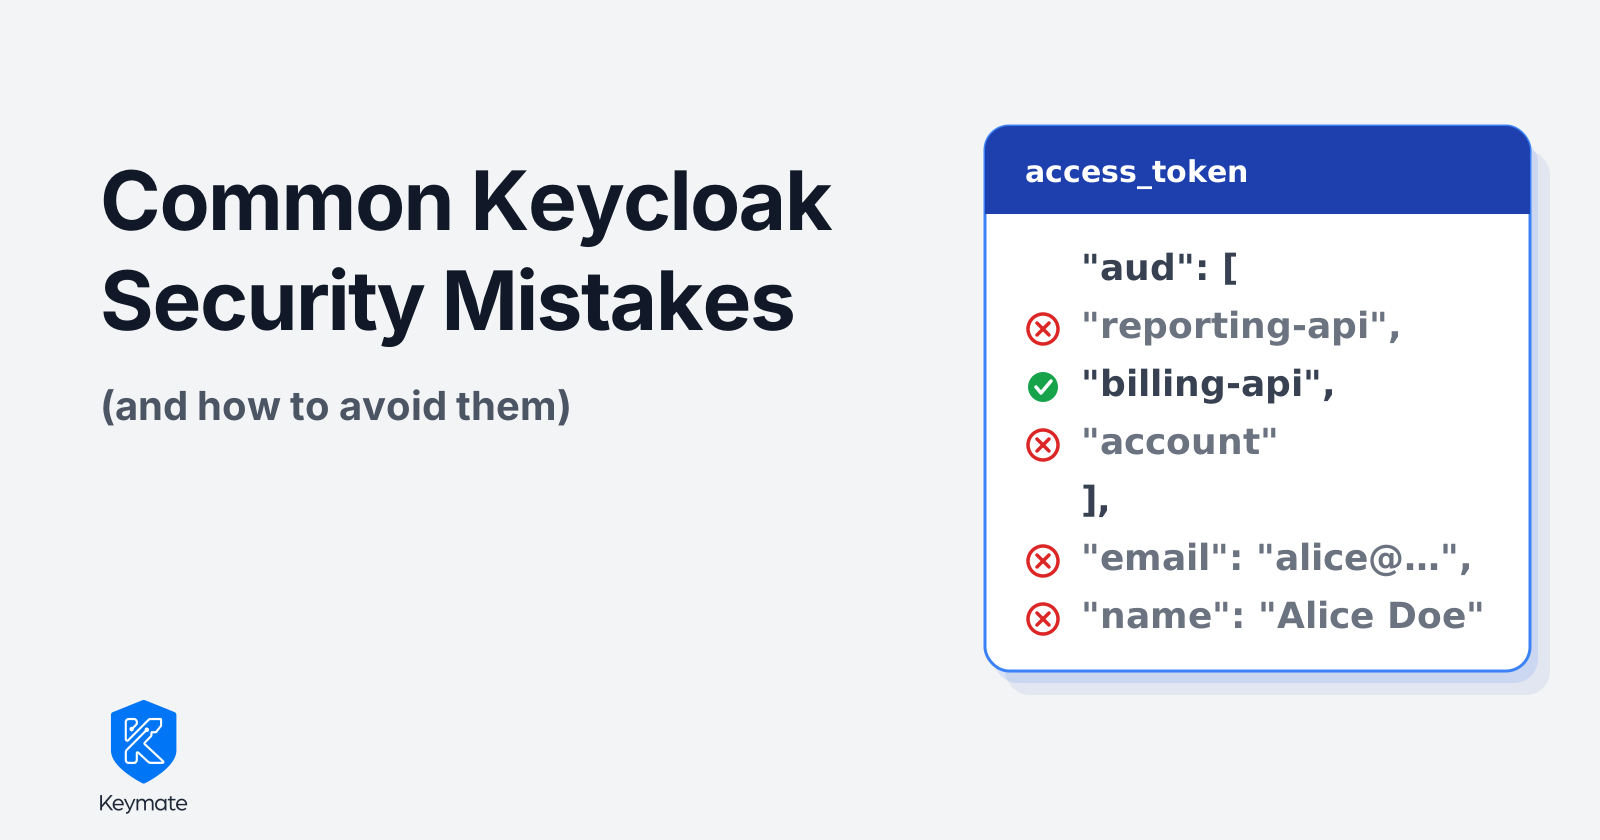
I logged in to a fresh Keycloak 26.8 realm and decoded the access token. Two backend clients would accept it, and checking the audience would not have stopped either one. Here are eight mistakes, most of them defaults, and how to fix them.

Muhammed Oğuz · Software Engineer
October 2026
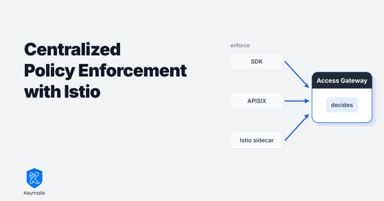
Centralized Policy Enforcement with IstioIstio can enforce an authorization decision at the sidecar. It should not be the place where that decision is made. Here is how a mesh enforcement point hands the decision to one central service, and what fails when the two stop agreeing.Buket Çoban
October 2026
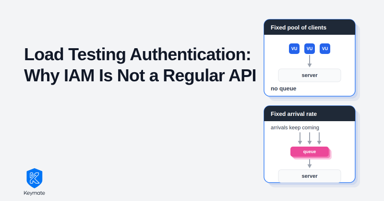
Load Testing Authentication: Why IAM Is Not a Regular APIA load test can report a healthy system and tell you nothing. Two settings inside the test decide the result before the server does, and the useful output is not a number but a number plus the conditions that produced it.Buket Çoban
September 2026
How Keycloak Password Policies WorkA password rule that only exists in your signup form is a suggestion, not a policy. Here is how Keycloak enforces password policies server-side, and which rules are worth enabling.Muhammed Oğuz
September 2026
Latest Posts
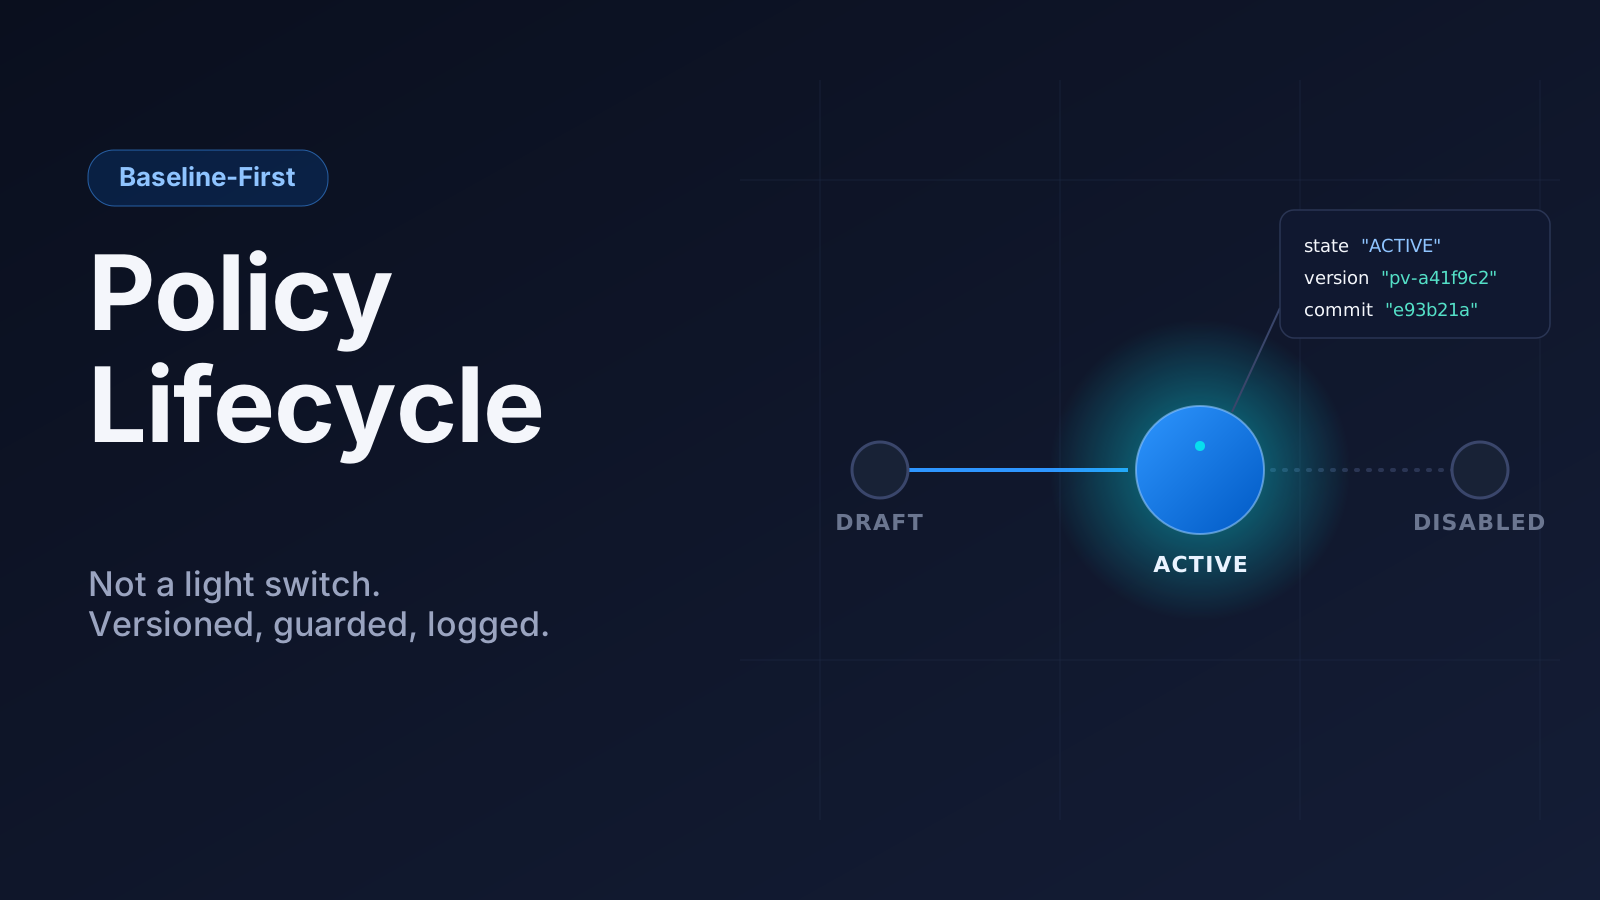
Policy Lifecycle: A Policy Change That Ships Like Code
Keycloak's built-in authorization services treat a policy like a config file you edit directly. Keymate treats it like a software release: versioned, guarded, and logged before it ships.Farhan Ahmed
August 2026
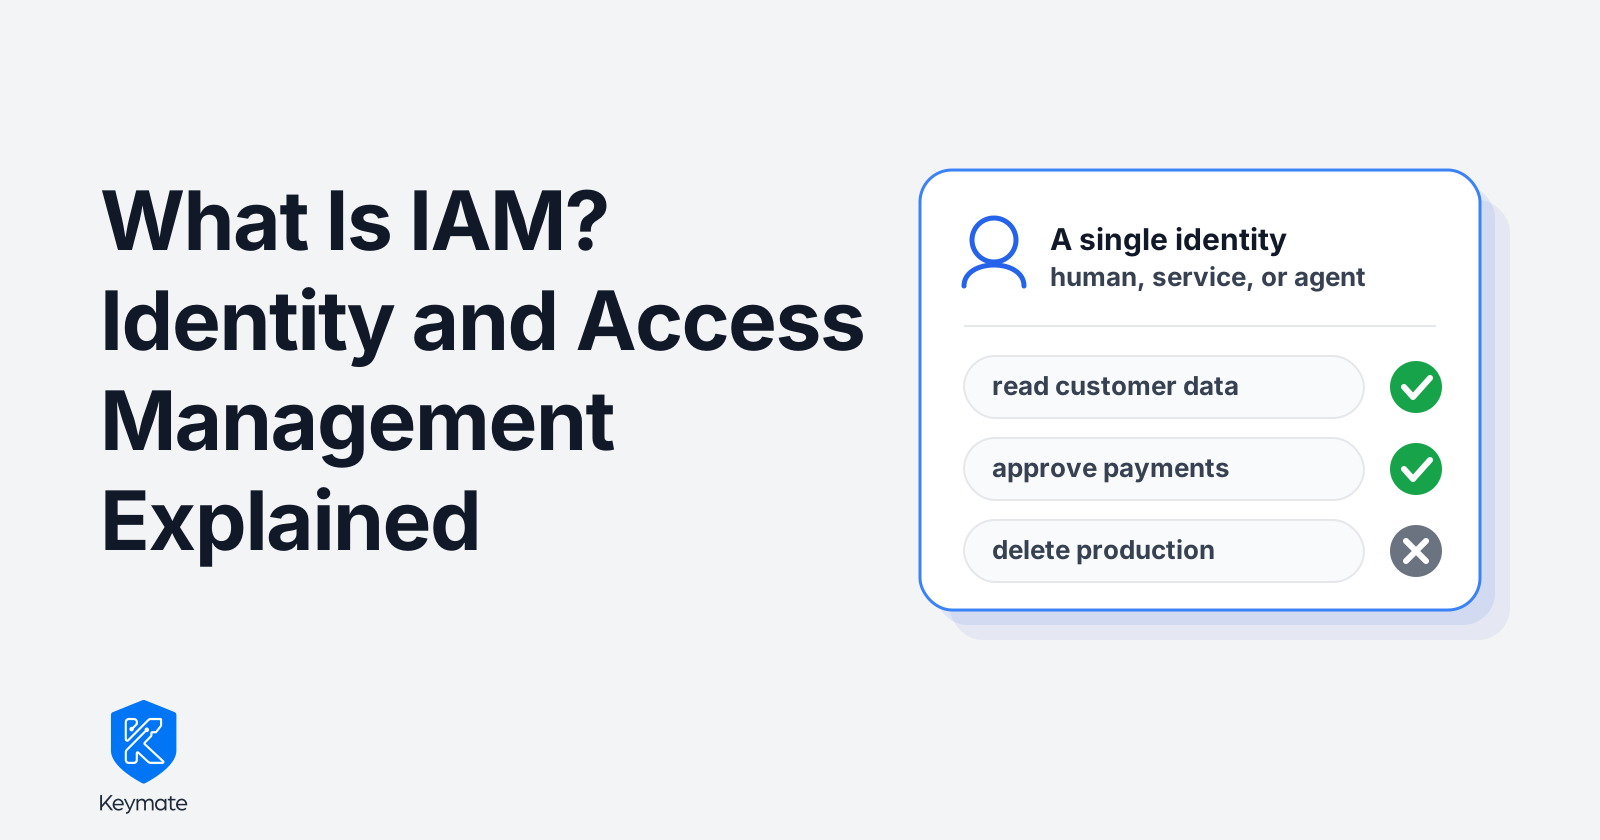
What Is IAM? Identity and Access Management Explained
Identity and access management decides who gets in, what they can touch once inside, and how you prove later that the decision was right. Here is the whole picture in one page: the vocabulary, the standards, the parts that break, and where access is actually decided.Israfil Coskun
August 2026
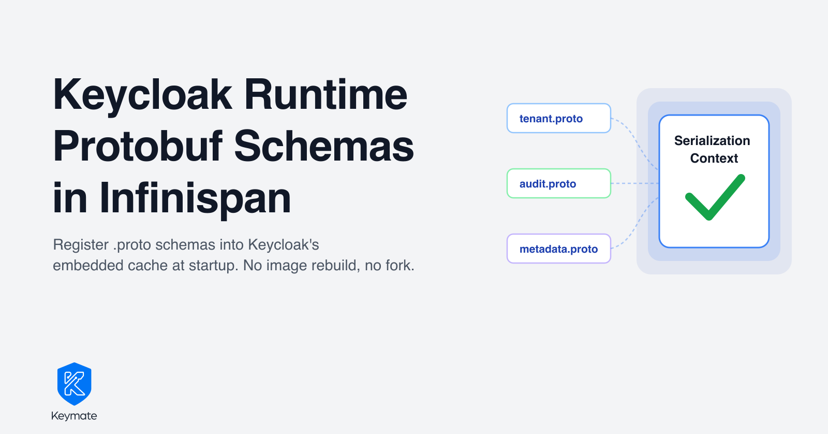
Runtime Protobuf Schemas in Keycloak's Embedded Infinispan
Keycloak offers no supported, configuration-only way to load runtime-mounted Protobuf schemas into its embedded Infinispan. This post walks through the extension pattern that bridges that gap through ProtoStream's documented initializer lifecycle, reviewed through a security and platform-engineering lens, with a runnable public demo.Ali Tuğrul Pınar
July 2026
Inside Keycloak Authorization: Resources & Policy Engine
A deep dive into Keycloak Authorization Services: how Resource Servers, Resources, Scopes, Policies, and Permissions fit together, and exactly how Keycloak decides permit or deny.Eren Kan
June 2026
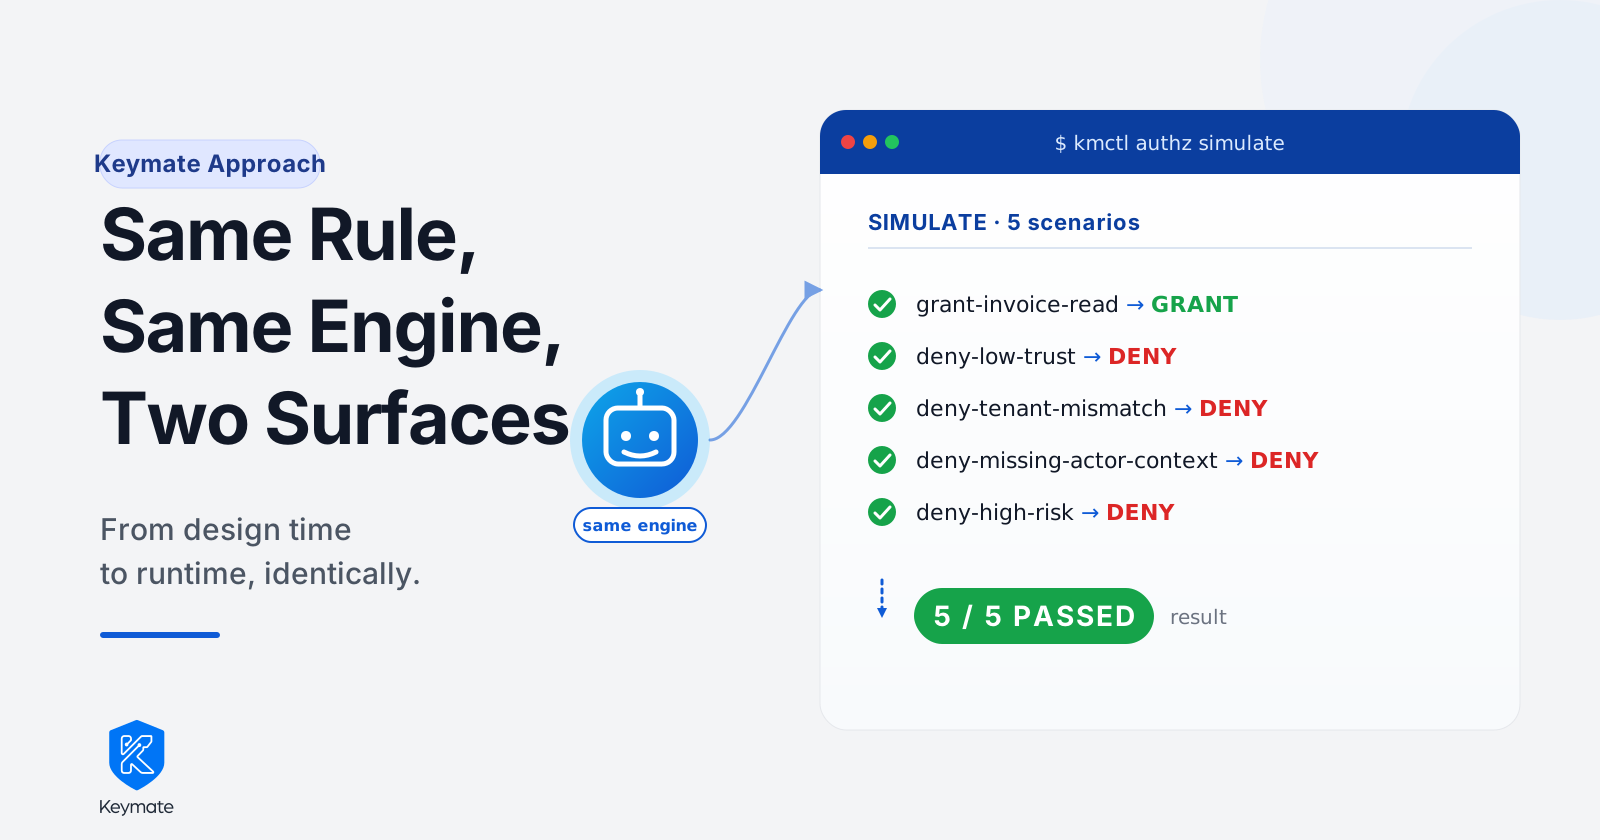
Fine-Grained Authorization for AI Agents: How It Works in Production
How Keymate enforces fine-grained authorization for AI agents: declarative policies, a centralized engine, and consistent design-time/runtime enforcement.Hüseyin Akdoğan
June 2026
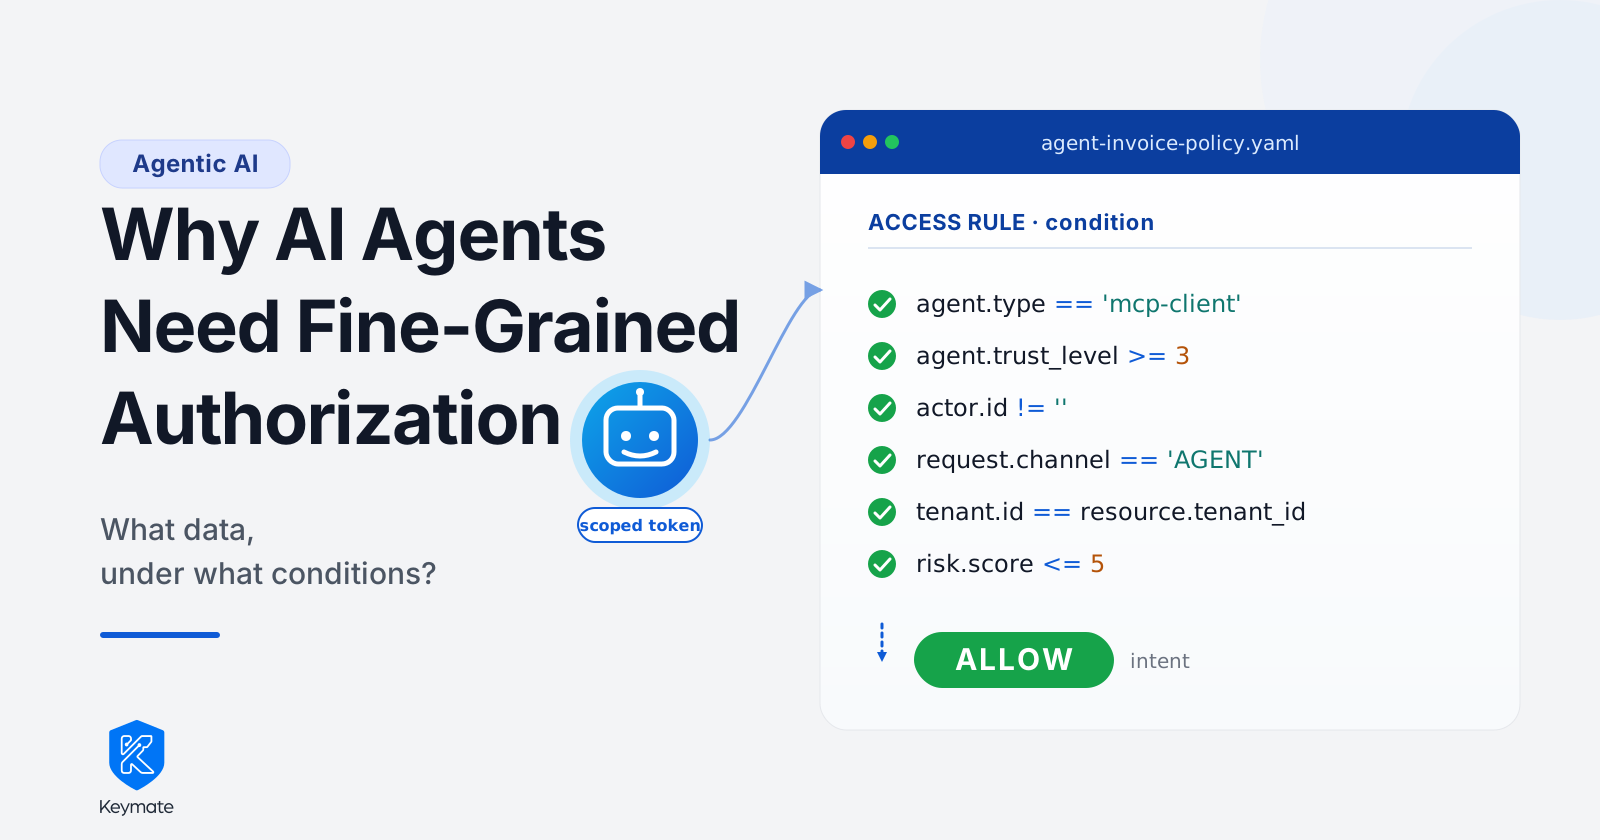
Why AI Agents Need Fine-Grained Authorization
Authentication tells us who the agent is. The harder question is what data it can reach, under what conditions, and on whose behalf. The April 2026 PocketOS incident, in which an autonomous coding agent deleted a production database in nine seconds, showed what happens when no one is answering it.Hüseyin Akdoğan
May 2026