Join our newsletter

New articles on Keycloak, authorization and running IAM in production.

  • ISO 27001

What is Keymate? Keymate is the authorization-first IAM platform. It is complete, self-hosted and built on hardened Keycloak, the CNCF open-source IAM project. Identity Governance and Authorization Governance are modules on top. Policies decide what each request may do. Keymate enforces that decision on every request. The record of each decision is what you show your auditor. It runs entirely on your infrastructure, air-gapped if you need it (Enterprise), and the product reports nothing back to us.

Product

  • Identity
  • Authentication
  • Authorization
  • Identity Governance
  • Authorization Governance
  • Parallel Run
  • Architecture
  • Roadmap
  • Pricing

Compare

  • IAM platform comparison
  • Keymate vs Okta
  • Keymate vs Microsoft Entra ID
  • Keymate vs Ping Identity
  • Keymate vs Keycloak

Why Keymate

  • Why Keymate
  • Access evidence for audits

Company

  • Company
  • Docs
  • Blog
  • Contributions
  • Careers
  • Support
  • Contact

© 2026 Keymate Inc. · the authorization-first IAM platform

  • Terms of Use
  • Privacy Policy
  • Cookie Policy
  • Information Security Policy
Keymate
  • Pricing
  • Blog
Book a demo

Keymate - Keymate Blog

Categories

Best PracticesDevOpsEngineeringGetting StartedIdentity & SecurityKeymatePerformanceSecurity
← Back to All Posts

Category: Keymate

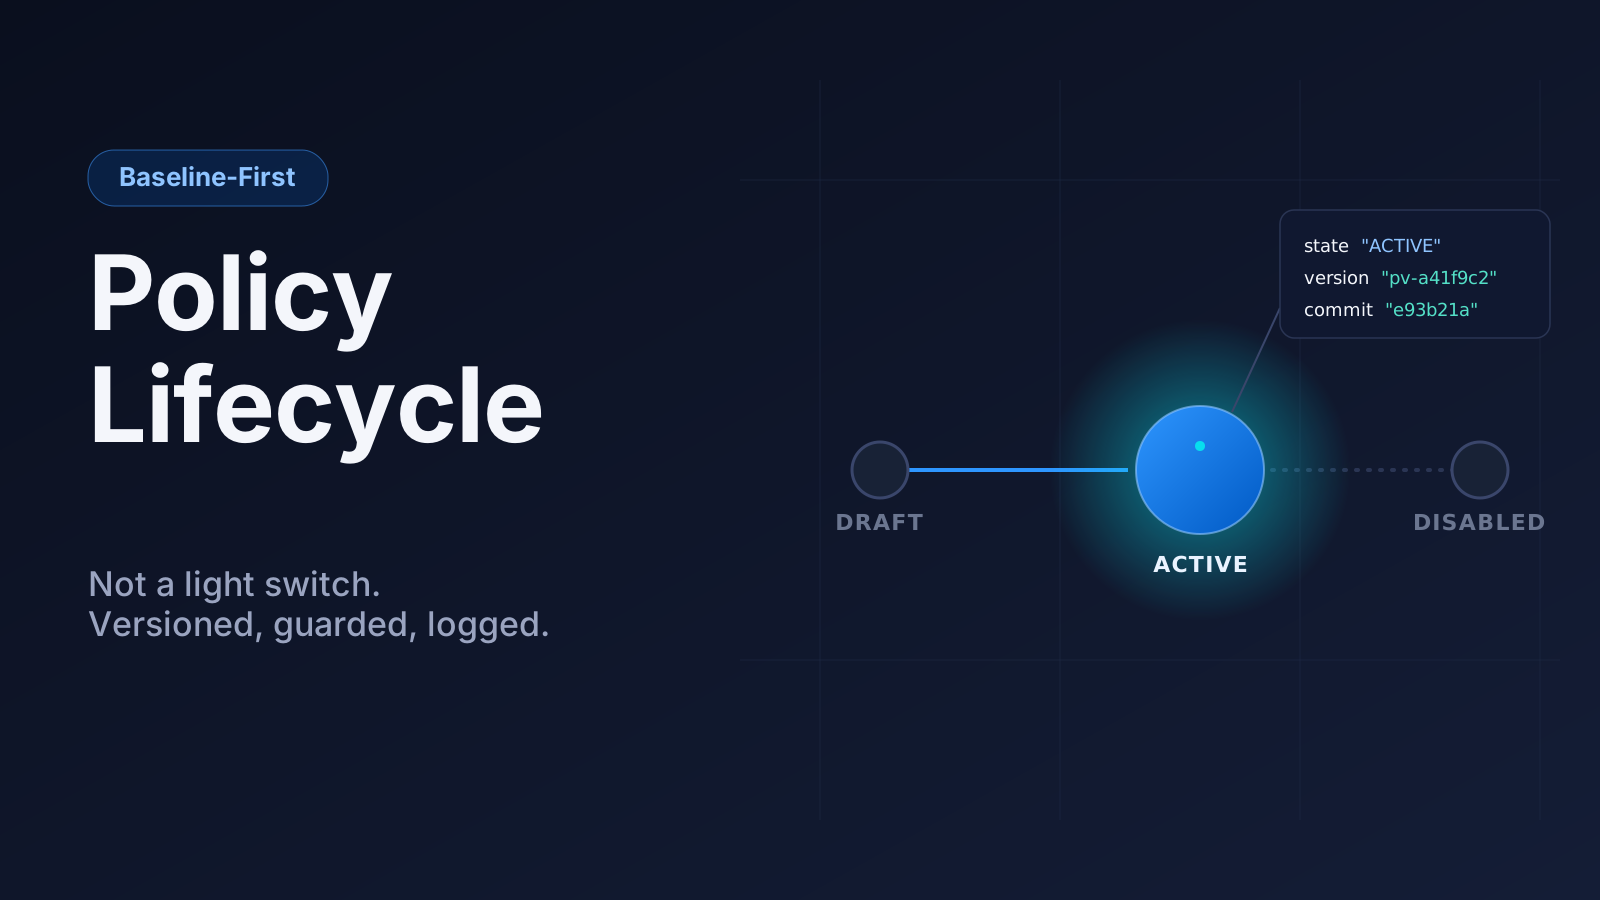
Policy Lifecycle: A Policy Change That Ships Like Code

Policy Lifecycle: A Policy Change That Ships Like Code

Keycloak's built-in authorization services treat a policy like a config file you edit directly. Keymate treats it like a software release: versioned, guarded, and logged before it ships.
Farhan Ahmed

August 2026

How Keymate Migrated 20+ Million Identities to Keycloak

How Keymate Migrated 20+ Million Identities to Keycloak

Migrating 20+ million identities is not a data copy problem. It is a controlled, observable, and failure-aware process. Learn how Keymate safely migrated a large-scale IAM system to Keycloak without downtime or silent data loss.
Hüseyin Akdoğan

December 2025

Multi-Tenancy & Delegation

Multi-Tenancy & Delegation

Roles tell who. Tenants and scopes tell where—and how far. Learn how to model multi-tenancy and delegated administration without role explosion or risky rewrites.
Halil Özkan

December 2025

The Limits of RBAC: Why Context Matters

The Limits of RBAC: Why Context Matters

RBAC is foundational—but at scale it breaks. Here’s why role explosion happens and how ABAC/ReBAC/RADAC complement RBAC without replacing your IAM.
Halil Özkan

October 2025

Why Keymate? How We Got Here

Why Keymate? How We Got Here

RBAC role explosion, multi-tenancy gaps, and opaque policy lifecycles keep biting enterprise IAM. Here is why we started Keymate and where this journey goes next.
Halil Özkan

September 2025